Have a Question?
Bridge Filter
| Document Date and version | 2021.02.22 |
| Tested with ONT HALNy HL-1GE/2, HL-1GC, HL-4G, HL-4GMV | Supported on Version: V2.0.18 or above |
| Tested with ONT HALNy HL-4GQV, HL-4GQVS/2, HL-4GXV/-F, HL-4GMV2/3/4 | Supported on Version: V3.0.12 or above |
| Tested with HALNy routers: HLE-3GM, HLE-3GX-F / HLE-4BX3V-F | Supported on Version: V3.0.12 / V5.0.9 or above |
| Tested with ONT HALNy HL-1B, HL-2BV, HL-4G2 | Supported on Version: V4.0.4 or above |
| Tested with ONT HALNy HL-4BX3V-F | Supported on Version: V5.0.9 or above |
Description
This function allows you to filter packets based on type for WAN interfaces in bridge mode. You can for example block multicast or IPv6 packets to not be forwarded in upstream/downstream or both direction.
Whole configuration is easy and can be done through web interface or XML provisioning.
INFO
Function works only with interfaces in brige mode (HGU).
Web configuration
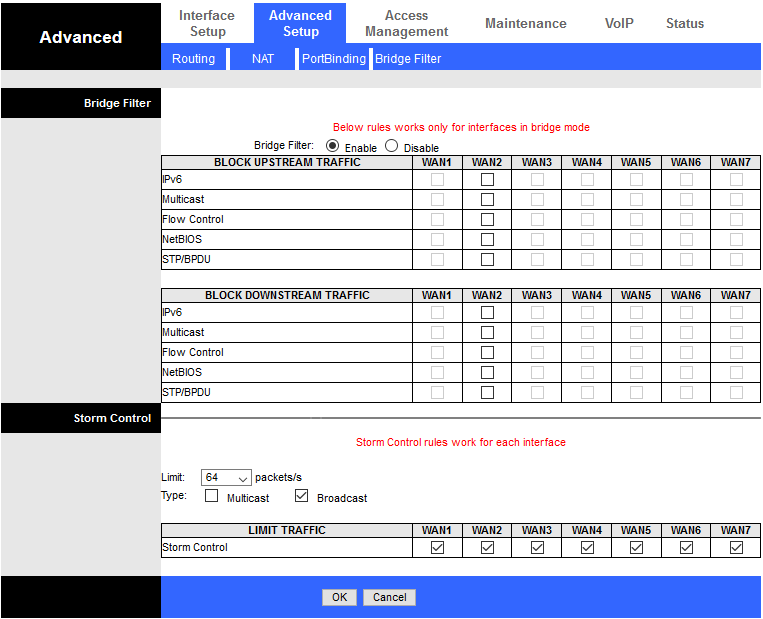
To configure this function go to Security -> Bridge Filter and choose the enable radio button. On the table below choose which type of packet do You want to filter and check the box for proper bridge interface (available here are only active bridge interfaces).
Firmware version V2.x.x
Firmware version V3.2.x/V4.x.x/V5.x.x

XML provisioning
To configure bridge filter through XML file, enter below attributes to section HALNyUniversalProvisioning -> HALNyConfiguration -> Other.
<BRIDGE_FILTER>
	<ENABLE_BRIDGE_FIREWALL>YES</ENABLE_BRIDGE_FIREWALL>
	<IPV6_UPSTREAM_BLOCK>WANX</IPV6_UPSTREAM_BLOCK>
	<IPV6_DOWNSTREAM_BLOCK>WANX</IPV6_DOWNSTREAM_BLOCK>
	<MULTICAST_UPSTREAM_BLOCK>WANX</MULTICAST_UPSTREAM_BLOCK>
	<MULTICAST_DOWNSTREAM_BLOCK>WANX</MULTICAST_DOWNSTREAM_BLOCK>
	<FLOWCONTROL_UPSTREAM_BLOCK>WANX</FLOWCONTROL_UPSTREAM_BLOCK>
	<FLOWCONTROL_DOWNSTREAM_BLOCK>WANX</FLOWCONTROL_DOWNSTREAM_BLOCK>
	<NETBIOS_UPSTREAM_BLOCK>WANX</NETBIOS_UPSTREAM_BLOCK>
	<NETBIOS_DOWNSTREAM_BLOCK>WANX</NETBIOS_DOWNSTREAM_BLOCK>
	<STP_BPDU_UPSTREAM_BLOCK>WANX</STP_BPDU_UPSTREAM_BLOCK>
	<STP_BPDU_DOWNSTREAM_BLOCK>WANX</STP_BPDU_DOWNSTREAM_BLOCK>
	<STORMCONTROL_BLOCK>WANX</STORMCONTROL_BLOCK>
	<STORMCONTROL_LIMIT>64|256|1024|4096</STORMCONTROL_LIMIT>
	<STORMCONTROL_MULTICAST>YES|NO</STORMCONTROL_MULTICAST>
	<STORMCONTROL_BROADCAST>YES|NO</STORMCONTROL_BROADCAST>
</BRIDGE_FILTER>ENABLE_BRIDGE_FIREWALL– enter YES to enable Bridge FilterIPV6_UPSTREAM_BLOCK... STP_BPDU_DOWNSTREAM_BLOCK– enter WANX, where X is the number of WAN interface.
You can set a couple of interfaces to one block rule, by separate them by “,” char – for example, to choose IPv6_UPSTREAM_Block rule for WAN1 and WAN2 interface enter:<IPv6_UPSTREAM_Block>WAN1,WAN2</IPv6_UPSTREAM_Block>STORMCONTROL_BLOCK– select interface which will be affected for storm control rules based on STORMCONTROL_MULTICAST or STORMCONTROL_BROADCAST configuration- In
STORMCONTROL_LIMITyou configure the number of broadcast packets that be limited if You enable StormControl rule (this attribute is necessary if You set StormControl_Block). You can enter here only 64, 256,1024, or 4096 packets/s. STORMCONTROL_MULTICASTandSTORMCONTROL_BROADCAST– enable or disable ratelimit rules for specific type of traffic
Type of filtered traffic
IPv6 – each packet of IPv6 based on the protocol IPv6 ethertype
Multicast – each packet based on destination MAC pattern 01:00:5e:70:00:00/ff:ff:ff:70:00:00
FlowControl – each packet based on destination MAC pattern 01:80:c2:00:00:01
NetBIOS – each packet based on destination port UDP:137,138 and TCP 139,445
StormControl – controls number of a broadcast/multicast packets per second
STP/BPDU – each packet based on destination MAC pattern 01:80:c2:00:00:00
| Found something we can improve? Let us know at support@halny.com |